Category: owa

  • OWA Error – There are too many active sessions connected to this mailbox

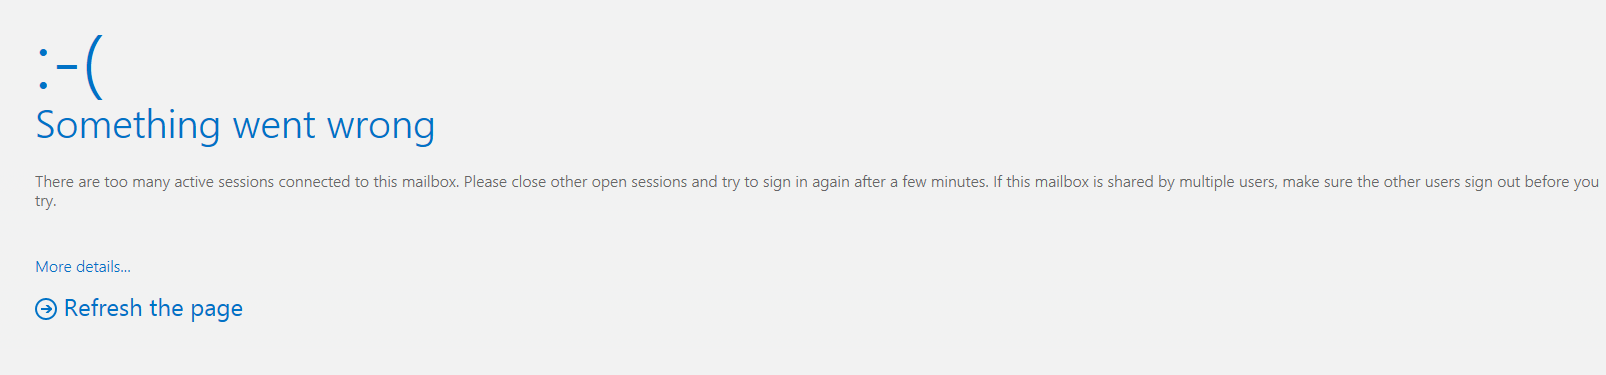
    Recently one of the shared mailbox which resides on Exchange 2016 while trying to access from web mail the users were getting the below error.

    This was a shared mailbox accessed by multiple team members.
    mm

    This issue happened for only one mailbox and it was fine for rest of the users.

    Looked into the IIS logs for the affected mailbox and there were multiple connections coming from different sources.

    IIS logs location can be found on below location
    C:\inetpub\logs\logfiles\W3SVC1

    Further looked  into the Event Viewer and found the event id 9646 with the below message for source MSExchangeIS
    Client Type OWA Exceeded the maximum objects of 16 per session
    So looked into the default connection OWA limit of the mailbox to see default values

    The Default value can be seen by running the below command

    Get-ThrottlingPolicy

    See the values of RcaMaxConcurrency and OwaMaxConcurrency for Global Throttling Policy and the Default Throttling Policy

    What is RcaMaxConcurrency ?

    The RcaMaxConcurrency is a parameter which controls how many Simultaneous parallel connections an RPC Client Access user can establish against an Exchange server at same time.

    These connections are considered when the server receives the request from the user until the connection is closed(Eg: The connection is considered as terminated only when the User closes the browser,goes offline,sign outs)
    If users attempt to make more concurrent requests than their policy allows, the new connection attempt fails. However, the existing connections remain valid.

    A valid value is an integer from 0 to unlimited. The default value is 40.

    What is OwaMaxConcurrency ?

    The OwaMaxConcurrency is a  parameter specifies how many concurrent connections an Outlook on the web user can have against an Exchange server at one time. A connection is held from the moment a request is received until a response is sent in its entirety to the requester. If users attempt to make more concurrent requests than their policy allows, the new connection attempt fails. However, the existing connections remain valid.

    The OwaMaxConcurrency parameter has a valid range from 0 through unlimited . The default value is 20. To indicate that the number of concurrent connections should be unthrottled (no limit), this value should be set to $null.

    Solution:
    Create a new policy with some more values for RcaMaxConcurrency and OwaMaxConcurrency and then assign some or all users to that rather than changing the default policy

    Create a new Throttling Policy
    New-ThrottlingPolicy -Name HighUsage -OwaMaxConcurrency 50 -RcaMaxConcurrency 100

    Apply this policy only to the affected users
    Set-Mailbox -Identity tonysmith -ThrottlingPolicy HighUsage

    There is one more method which will override the default throttling policy which can be applied on the registry but this will be applicable for all mailboxes :

    Locate and then click the following key in the registry:
    HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\MSExchangeIS\ParametersSystem
    On the Edit menu, point to New, and then click DWORD Value.
    Type Maximum Allowed Service Sessions Per User, and then press ENTER.
    On the Edit menu, click Modify.
    Type the decimal value that specifies the number of sessions that you want to use, and then click OK.
    Exit Registry Editor.

    Since this will be applicable for all mailboxes better to avoid this registry entry.

    Note:
    For the above behavior as a first step its always better to reach the affected end user , verify from how many devices and PC he has connected, Try to disable and re-enable the owa feature for a while and see the results. If still we keep getting the event id 9646 for the affected user then we can create a throttling policy and assign the user to the policy.

    Thanks & Regards
    Sathish Veerapandian
    MVP – Office Servers & Services 

  • Exchange 2013 Unable to access ECP Encounter “500 Unexpected Error”

    Today i faced an issue in accessing ecp  through an admin delegated account and got the below error. I thought of writing up a blog with few general checklists that can be performed if we come across this kind of issues.

    ECP

    Below are the troubleshooting  steps that can be performed in this order if we come across  issues with accessing the ECP virtual directory.

    1) Check if there is any issue with the XAML file type

    Find the file located in

    C:\Program Files\Microsoft\Exchange Server\V15\ClientAccess\ecp\DDI\RemoteDomains.XAML

    XAML

    If you have any staging servers with the same version where it is working just copy this XML file or if you could find this file from the setup just replace with the existing one do an iis reset and see the results

    2) Check on the Application Pools to view whether OWA and ECP Application Pool is running on .NET Framework v4.0. It maybe the incompletely or corrupted installation of Framework that causes this error.

    APP

    You might come across the above if you recently made any recent upgrade or its a new fresh installation.

    If that’s the case try to run the following command as Administrator:

    %windir%\Microsoft.NET\Framework\v4.0.30319\aspnet_regiis.exe -i

    Change the MSExchangeECPAppPool from .NET Framework from v4.0 to v2.0. Then restart IIS and check the results.

    XAML2

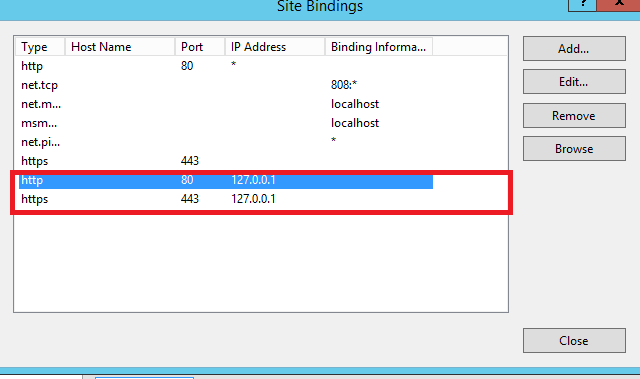
    3) Check the bindings of the default website to confirm to Microsoft recommended settings:

    ({http port 80 *}{http port 80 127.0.0.1}
    {https port 443 *}{https port 443 127.0.0.1})

    XAML3

    4) If none of the above steps works try recreating the ecpvirtualdirectory and see the results

     In EMS, please run the following command:

    Remove-Ecpvirtualdirectory –Identity “CAS\Autodiscover (xxxxx)”

    New-Ecpvirtualdirectory –Identity “CAS\Autodiscover (xxxxx)”

    There are more cases where even recreating the ECP virtual directory or any virtual directory will still cause this same error 500 unexpected error

    This is because of the stale entries present in the ecp objects as well as in the IIS metabase.

    If recreating corresponding affected VD doesn’t help you then  try the below steps

    Remove the newly created ECP virtual directory

    Remove-Ecpvirtualdirectory –Identity “CAS\ECP(xxxxx)”

    5)  Remove the ecp objects in AD container

    a. Open ADSIEDIT.msc, locate:

    Configuration–>CN=Services–>CN=Microsoft Exchange–>CN=Organization–>CN=Administrative Groups–>CN=Exchange Administrative Groups–>CN=Servers–>CN=Exchange–>CN=Protocols–>CN=HTTP

    b. In the right pane, please check whether the CN=ECP(xxx) is present. If its present you can remove it.

    XAML4

    6. Delete the autodsicover in metabase

    a. Download the IIS 6.0 Resource Kit Tools from the following link:

    http://www.microsoft.com/downloads/en/details.aspx?FamilyID=56fc92ee-a71a-4c73-b628-ade629c89499&displaylang=en

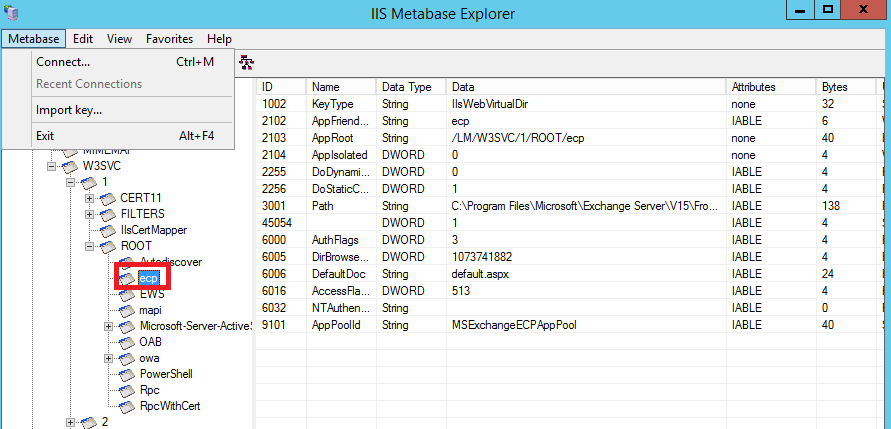
    b. Install it on the CAS server. Open the “Metabase Explorer” (Open it in elevated mode)

    c. Locate: Exchange -> LM -> W3SVC -> 1 -> ROOT.

    XAML5
    d. Check if you are able to find ECP virtual directory  is present, if so, remove it.

    7. After that, try recreating the ECP virtual directory and see the results

    New-Ecpvirtualdirectory –Identity “CAS\Autodiscover (xxxxx)”

    Most likely after following the above troubleshooting steps the affected ECP VD should start working. You can also follow the same troubleshooting steps if in case  you are getting the same error in accessing the OWA,EAC ,Autodiscover and PowerShell Virtual Directories.

    Hope this article is helpful

    Thanks 

    Sathish Veerapandian

    MVP – Exchange Server

  • Error – “Something went wrong” in both OWA and ECP

    After applying updates on Exchange 2013 environment we might come across the below symptom  from end users while accessing OWA

    User can use outlook to send/receive emails normally, but when the user try to login OWA, a “something went wrong” screen with the following information appears:


    owa

    An unexpected error occurred and your request couldn’t be handled.

    X-OWA-Error: System.NullReferenceException

    X-OWA-Version: 15.0.775.32

    X-FEServer: {2013 CAS server}

    X-BEServer: {2013 Mailbox server}

    Date: **

    1) Rebuilding OWA/ECP virtual directories will not help

    2) Playing with owa authentication settings will not help

    3) Re-installing exchange server also will not help at times


    While looking into the event logs you can find the below log with the description


    ev

    Description        :
    Event code: 3005
    Event message: An unhandled exception has occurred.
    Event time: 8/30/2013 11:02:13 AM
    Event time (UTC): 8/30/2013 4:02:13 PM
    Event ID: f959d55d927a45f8b3b69051bbd62038
    Event sequence: 2
    Event occurrence: 1
    Event detail code: 0

    Application information:
    Application domain: /LM/W3SVC/2/ROOT/owa-1-130223042171473642
    Trust level: Full
    Application Virtual Path: /owa
    Application Path: C:\Program Files\Microsoft\Exchange Server\V15\ClientAccess\owa\
    Machine name: EXC2013CAS

    Process information:
    Process ID: 13764
    Process name: w3wp.exe
    Account name: NT AUTHORITY\SYSTEM

    Exception information:
    Exception type: NullReferenceException
    Exception message: Object reference not set to an instance of an object.
    at Microsoft.Exchange.Clients.Common.Canary15.Init(Byte[] userContextIdBinary, Byte[] timeStampBinary, String logonUniqueKey, Byte[] hashBinary, String logData)
    at Microsoft.Exchange.Clients.Common.Canary15..ctor(String logonUniqueKey)
    at Microsoft.Exchange.Clients.Common.Canary15Cookie.TryCreateFromHttpCookie(HttpCookie cookie, String logonUniqueKey, Canary15Profile profile)
    at Microsoft.Exchange.Clients.Common.Canary15Cookie.TryCreateFromHttpContext(HttpContext httpContext, String logOnUniqueKey, Canary15Profile profile)
    at Microsoft.Exchange.Clients.Owa2.Server.Core.OwaRequestHandler.InternalOnPostAuthorizeRequest(Object sender)
    at Microsoft.Exchange.Clients.Owa2.Server.Core.OwaRequestHandler.OnPostAuthorizeRequest(Object sender, EventArgs e)
    at System.Web.HttpApplication.SyncEventExecutionStep.System.Web.HttpApplication.IExecutionStep.Execute()
    at System.Web.HttpApplication.ExecuteStep(IExecutionStep step, Boolean& completedSynchronously)

    Request information:
    Request URL: https://localhost:444/owa/logoff.owa
    Request path: /owa/logoff.owa
    User host address: 127.0.0.1
    User: CORJESU\SM_cab26786a5604c759
    Is authenticated: True
    Authentication Type: Kerberos
    Thread account name: NT AUTHORITY\SYSTEM

    Thread information:
    Thread ID: 12
    Thread account name: NT AUTHORITY\SYSTEM
    Is impersonating: False
    Stack trace:    at Microsoft.Exchange.Clients.Common.Canary15.Init(Byte[] userContextIdBinary, Byte[] timeStampBinary, String logonUniqueKey, Byte[] hashBinary, String logData)
    at Microsoft.Exchange.Clients.Common.Canary15..ctor(String logonUniqueKey)
    at Microsoft.Exchange.Clients.Common.Canary15Cookie.TryCreateFromHttpCookie(HttpCookie cookie, String logonUniqueKey, Canary15Profile profile)
    at Microsoft.Exchange.Clients.Common.Canary15Cookie.TryCreateFromHttpContext(HttpContext httpContext, String logOnUniqueKey, Canary15Profile profile)
    at Microsoft.Exchange.Clients.Owa2.Server.Core.OwaRequestHandler.InternalOnPostAuthorizeRequest(Object sender)
    at Microsoft.Exchange.Clients.Owa2.Server.Core.OwaRequestHandler.OnPostAuthorizeRequest(Object sender, EventArgs e)
    at System.Web.HttpApplication.SyncEventExecutionStep.System.Web.HttpApplication.IExecutionStep.Execute()
    at System.Web.HttpApplication.ExecuteStep(IExecutionStep step, Boolean& completedSynchronously)


    By looking into the event viewer we can see this is related to Active Directory Cache error related with CAS server for a value called Canary Data

    What is this Canary Data ?
    Basically Canary Data is an attribute that is created during the first exchange 2013 schema preparation.

    It creates 4 attributes while schema preparation or it may be even just one attriubute

    msExchCanaryData0
    msExchCanaryData1
    msExchCanaryData2
    msExchCanaryData3

    Why do we need this Canary Data ?

    It is a secret token that exchanges between the clients and the server for services OWA,ECP and other exchange web services.

    So these values gets stored in the cookie collection of the clients browser.

    So for any owa,ECP,EWS requests from clients the browser sends the GUID value that is stored in the cache and compares it with the GUID that is in the URL (server).
    If they dont match then the request from the client is considered as malicious and blocked
    Also an event regarding the same is logged with the originating IP address.

    Below is the solution to fix this type of issue :


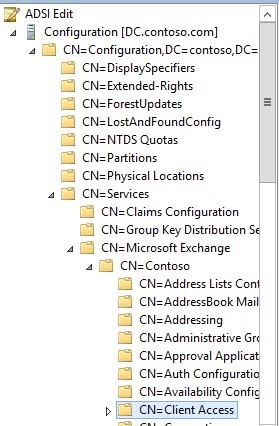
    1) Open ADSI Edit

    ADS

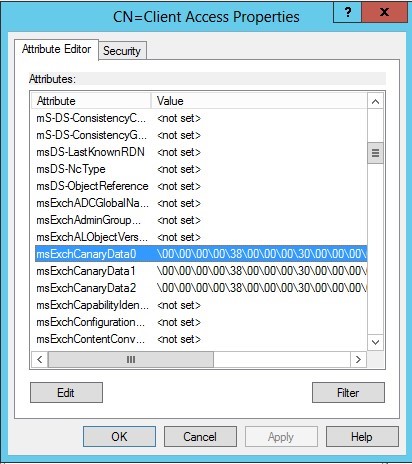
    2) Right click 【CN=Client Access】and click properties, scroll down to look for values

    【msExchCanaryData0】

    【msExchCanaryData1】

    【msExchCanaryData2】

    【msExchCanaryData3】

    parameter, as below:

    ADS2


    3) Take a backup to be safe and clear all these values to not set as shown below

    ADS3

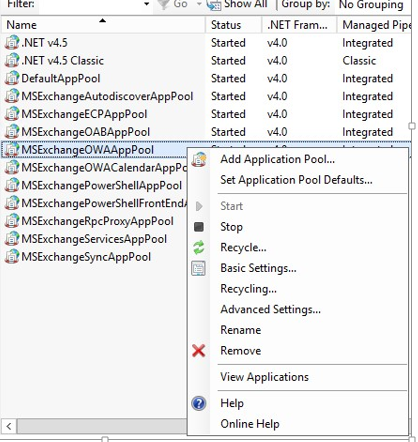
    4.Open IIS Manager on your CAS server, go to 【Application Pools】, right click 【MSExchangeOWAAppPool】 and click Recycling


    ADS4


    After doing the above its better to restart Mailbox and CAS server and this issue will be resolved.

    Also Refer –

    http://social.technet.microsoft.com/wiki/contents/articles/29433.error-something-went-wrong-in-both-owa-and-ecp.aspx

    Thanks

    Sathish Veerapandian

    MVP – Exchange Server

  • OWA,EWS configuration in Exchange 2013/2007 coexistence

    We need to consider few factors while planning for coexistence between Exchange 2013 and legacy exchange servers especially exchange 2007 .We might run into few confusions. In this article i will mention few key points which needs to be considered while planning Exchange 2007 and 2013 coexistence for owa,ews setup.

    In coexistence with exchange 2013 and legacy version the request happens in 2 types.
    For Exchange 2010 – Exchange 2013 does a Proxy for owa and ews requests for users in exchange 2010.
    For Exchange 2007 – Exchange 2013 does redirection for owa and ews requests for users in Exchange 2007.

    When a user with an Exchange 2007 mailbox logins externally from OWA the requests goes to Exchange 2013. Now the Exchange 2013 needs this connection to be redirected to exchange
    2007 server.

    In Order to do this Exchange 2013 requires a dedicated external host name configured on exchange
    2007 server’s for the required services accessed from externally. So the external and internal hostnames of the Exchange 2007 server need to be different from the hostnames of the Exchange 2013 server and need to be pointed to the Exchange 2007 server.

    Better use the Exchange Server Deployment Assistant which will give much clear information.If
    you are still confused then you can remember the following key points.

    First all the services URL’s needs to be pointed to Exchange 2013 CAS server from exchange
    2007.Exchange 2013 CAS server will redirect the connections to Exchange 2007 server.

    Legacy Names:
    Configure following Legacy host names for the below services in exchange 2007

    OwaVirtualDirectory – Create https://ExternalLegacyHostName/owa
    WebServicesVirtualDirectory – Create https://ExternalLegacyHostName/EWS/Exchange.asmx
    UMVirtualDirectory – Create https://ExternalLegacyHostName/UnifiedMessaging/Service.asmx
    OABVirtualDirectory – Create  https://ExternalLegacyHostName/OAB
    ActiveSyncVirtualDirectory – Create  https://InternalLegacyHostName/Microsoft-Server-ActiveSync


    Planning Internal and External owa URL’s

    For Exchange 2013 OWA URL: Use same old URL for OWA access to Exchange 2013 and change the IP address from exchange 2007 to E15 internally.
    Change the external owa url and redirect the connections to exchange 2013 CAS.

    For Exchange 2007 OWA URL:

    Create Legacy. Domain.com for external owa users.
    Create Legacy.Domain.com for internal owa users.

    Below is an example to Modify the OWA url :

    On Exchange 2013 point the ExternalUrl  ‘mail.contoso.com’ to Exchange internet facing CAS server.
    On Exchange 2007 create the ExternalUrl as ‘legacy.contoso.com’


    Certificates:

    All the required SAN entries for UM,webservices and activesync should be created.
    Add external owa legacy URL to the public certificate and install it on both Exchange 2007 and
    Exchange 2013 only then owa redirection will work.
    You need to Include internal Legacy. Domain.com on Exchange 2007 Certificate for OWA co-
    Existence.
    Following change needs to be done in Firewall

    External OWA URL should be directed to exchange 2013 Internet Facing CAS.

    External EWS URL should be directed to  exchange 2013 Internet Facing CAS.

    External Autodiscover URL should should be directed to  Exchange 2013 CAS.
    External ActivesyncVirtualDirectory should be directed to Exchange 2013 CAS.

    External UMvirtualDirectory should be directed to  Exchange 2013 CAS.

    Create new NAT rule on firewall for Legacy.domain.com to Exchange 2007 CAS. You can do this as well.By doing this users will be able to log on directly using the URL https://legacy.domain.com/owa with a mailbox on Exchange 2007.


    External and Internal DNS settings

    Public DNS – Map all of your external public DNS records (ews,owa,activesync etc.,) to your
    exchange 2013 public IP if you have dedicated one for 2013 or FQDN of your internet facing CAS server.
    Example:
    Current external owa URL (contoso.domain.com) – point it to dedicated exchange 2013 public ip or internet facing exchange 2013 CAS FQDN.
    Current External Autodiscover – point it to dedicated exchange 2013 public ip or internet
    facing exchange 2013 CAS FQDN

    Internal DNS – Configure the Exchange 2007 to point SCP AutoDiscoverURI to Exchange 2013 Client
    Access FQDN by changing DNS entry for Autodiscover.domain.com to exchange 2013 CAS sever Ip
    address

    The internal DNS records should point to the internal host name and IP address of your Exchange
    2013 Client Access server
    Make sure that legacy.contoso.com resolves to CAS2007 in internal and external DNS.

    Authentication Settings:

    This part is little bit tricky. You need to plan according to your organization. If you have FBA configured in TMG or ISA server then you need to configure accordingly.
    Set the owa virtual directory authentication only to  Basic in exchange 2007.
    In exchange 2013 set owa virtual directory to only (Windows Authentication) or only (form-based authentication) or only (Basic, No redirection, SSL Enabled) depends according to your setup.

    Things to check:

    If you have redirection configured in IIS on the Exchange 2007 Server Make sure that the above
    Virtual Directories doesn’t have it configured.

    If you have FBA enabled on ISA or TMG then disable FBA on Exchange 2013 CAS else users will be prompted twice for authentication.

    References:

    http://technet.microsoft.com/en-us/library/jj898581(v=exchg.150).aspx

    Checklist: Upgrade from Exchange 2007
    http://technet.microsoft.com/en-us/library/ff805032(v=exchg.150).aspx

    Install Exchange 2013 in an Existing Exchange 2007 Organization
    http://technet.microsoft.com/en-us/library/jj898582(v=exchg.150).aspx

    http://blogs.technet.com/b/meamcs/archive/2013/07/25/part-2-step-by-step-exchange-2007-to-2013-migration.aspx

    Thanks

    Sathish Veerapandian